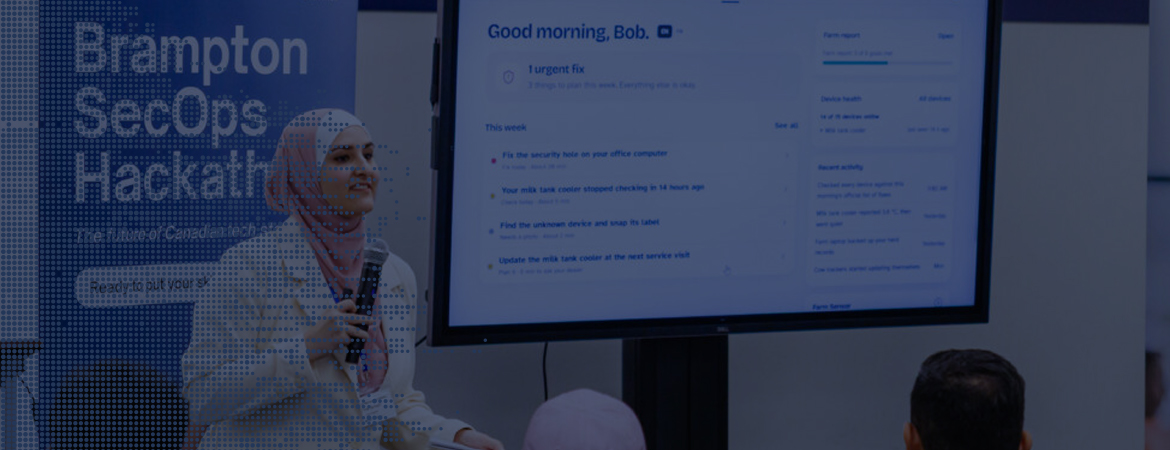
From September 25 to 27, 2026, Rogers Cybersecure Catalyst hosted the Brampton SecOps Hackathon 2026 at its Brampton location. It was the Catalyst's first hackathon. Over three days, teams of students and recent graduates took on two real cybersecurity problems facing Canada's agri-food and multimodal logistics sectors. I took part twice: as a panelist at the Friday kick-off and as a judge at Sunday's finals.
It was a weekend of long hours, fast learning and some promising ideas in agri-food cybersecurity. It also taught the teams, the judges and the organizers a few useful lessons.
Brampton is one of Canada's busiest trucking and distribution hubs, which makes logistics cybersecurity a local concern as much as a technical one. The Greater Toronto Area is also the country's leading hotspot for cargo theft. Ontario recorded more than 1,600 cargo and trailer thefts in 2025, according to Équité Association, and deceptive pickups, where someone poses as a real carrier, are a growing share of cargo theft.
Food and agriculture face the same pressure. The Food and Ag-ISAC tracked 227 ransomware attacks on the sector through July 2026, a 62% increase over the same period last year. When a food processor or distributor loses its ordering and shipping systems, the result is not a data breach report. It is spoiled product, idle trucks and empty shelves.
The two challenges reflected this:
At the kick-off panel, our goal was to give teams enough supply chain cybersecurity context to scope a useful solution in a short time. Three ideas came up again and again:
It was encouraging to see these ideas in the finalists' work two days later.
Seven teams reached the finals, split evenly between the two challenges. Instead of singling out teams, here are the themes they explored, because together they show where the real needs are.
Several teams focused on the moments when goods or money change hands: a driver arriving at a dock, a late change to a delivery address, or a request to update payment details. Their ideas ranged from checks inside the email inbox to mobile verification at pickup and multi-person approval of changes. The shared principle: verify a request before anyone acts on it, using contact details already on file, not the ones in the message.
Other teams built self-assessment tools that bring cybersecurity for small businesses down to plain language. Questionnaires became dashboards and prioritized action lists. The better ones went beyond office IT to cover the equipment that keeps the operation running, such as cold rooms, production lines and connected farm equipment.
Some of the best work came from teams that looked past the obvious targets. Dairy farms and aquaculture operations depend more and more on connected equipment, often with little or no IT support, and agri-food cybersecurity rarely reaches them.
The stronger entries understood that a small operator needs help fixing problems, not just a list of them. They connected their tools to IT support providers, insurers or existing industry workflows.
The winning teams stood out for one reason. They picked a specific user, understood that person's day and built something that fit into it. Several spoke directly with drivers, dispatchers and farmers during the weekend, and it showed.
Judging seven teams side by side makes patterns easy to see. The winners brought solid ideas, and the judging panel also agreed there is room to go from good to great. None of this is criticism of the participants. These are opportunities for teams, organizers and judges alike.
Both challenges were broad on purpose, which gave teams freedom. The trade-off is that broad problems invite broad answers. Some solutions could have worked for almost any small business, with agri-food added as a use case. The strongest teams narrowed the problem themselves to one person, one moment and one failure. Future challenges could do some of that narrowing up front, for example with a concrete scenario at a cold storage warehouse or a regional carrier.
Teams had about 48 hours to form, brainstorm, build a prototype, write a go-to-market plan and give a ten-minute pitch. That showed in rushed demos and business models that needed more time. A longer format, or sharing problem briefings and industry contacts before the event, would let teams spend more time on the part that matters most: understanding the problem.
Technical depth had the most room to improve. Many prototypes had a clean interface and a clear workflow, but little of the logic underneath. How does the tool decide a request is suspicious? What happens when a real, urgent request gets flagged? Where do the metrics and formulas come from? As one fellow judge put it, showing value means showing how the product behaves when a real event happens. Demonstrating a failure and how the tool handles it is often more convincing than a perfect run.
AI helped teams build more in less time, which is a real advantage. But when many decks and scripts are generated the same way, the pitches start to sound alike. The ones that stood out felt personal: a conversation with someone in the industry, a real story from the field or a hand-built slide deck. Judges remember the team's own insight, not the polish.
It was the first hackathon hosted by Rogers Cybersecure Catalyst at its Brampton location, held from September 25 to 27, 2026. Student and recent graduate teams spent three days building solutions for cyber risks in Canada's agri-food and logistics sectors.
Food moves on tight schedules. When ordering or shipping systems go down, the loss is spoiled product, idle trucks and empty shelves, not just lost data.
It is the protection of the links between partners, such as carriers, suppliers and buyers, so that a fake request or a compromised system at one company does not spread to the others.
Start with a short, ordered list of actions. The most useful first step is to verify any change to a pickup location or payment details using contact information you already have on file. This is the practical core of cybersecurity for small businesses in this sector.
The organizations most exposed to supply chain cybersecurity risk often have the fewest resources to deal with it. Small carriers, processors and farms will not be protected by enterprise tools built for security teams they do not have. They will be protected by simple, practical solutions built by people who understand how their work gets done.
That weekend showed that the talent and interest are there. With sharper problem statements, a little more time and a stronger focus on the end user, the next edition could produce solutions ready for a real pilot.
Thank you to Rogers Cybersecure Catalyst for organizing, to the mentors and fellow judges for their time, and to every team that spent a weekend on problems that matter to Canada's food supply. Actimeta was glad to be part of it. If your own operation needs help with industrial or OT cybersecurity, talk to Actimeta, an OT cybersecurity company based in Toronto.
